Sunday, August 2, 2026

The CLARITY Act Is Not Stalling Over Crypto

BitBrainers - The CLARITY Act Is Not Stalling Over Crypto

By BitBrainers Editorial

The Senate leaves for its August recess in under a week and the most consequential crypto bill in US history still has no floor vote scheduled. It is not stalling over how to regulate digital assets. Every serious version of that fight was settled months ago. It is stalling over whether the sitting President should be allowed to keep earning from the industry the bill would legitimise.

Where It Actually Stands

The Digital Asset Market Clarity Act passed the House on 17 July 2025 by 294 to 134. The Senate Banking Committee advanced its portion on 14 May 2026 by 15 to 9. Since then: no floor vote, no cloture filed, no scheduled date.

The bill has been sitting on the Senate Legislative Calendar since 1 June, at number 423. Eligible for floor action for two months, never scheduled.

Industry and congressional negotiators marked 7 August as the practical deadline. Majority Leader John Thune told reporters he did not think they would get it done, adding that he would like to at least get CLARITY started.

The arithmetic is the whole problem. Republicans hold 53 seats. Cloture needs 60. That means at least seven Democrats, and under Senate Rule XXII the bill needs two separate cloture sequences, each of which typically eats most of a legislative week. Floor time that might have covered it went to a Russia sanctions package and a backlog of nominations.


What Is Actually in It

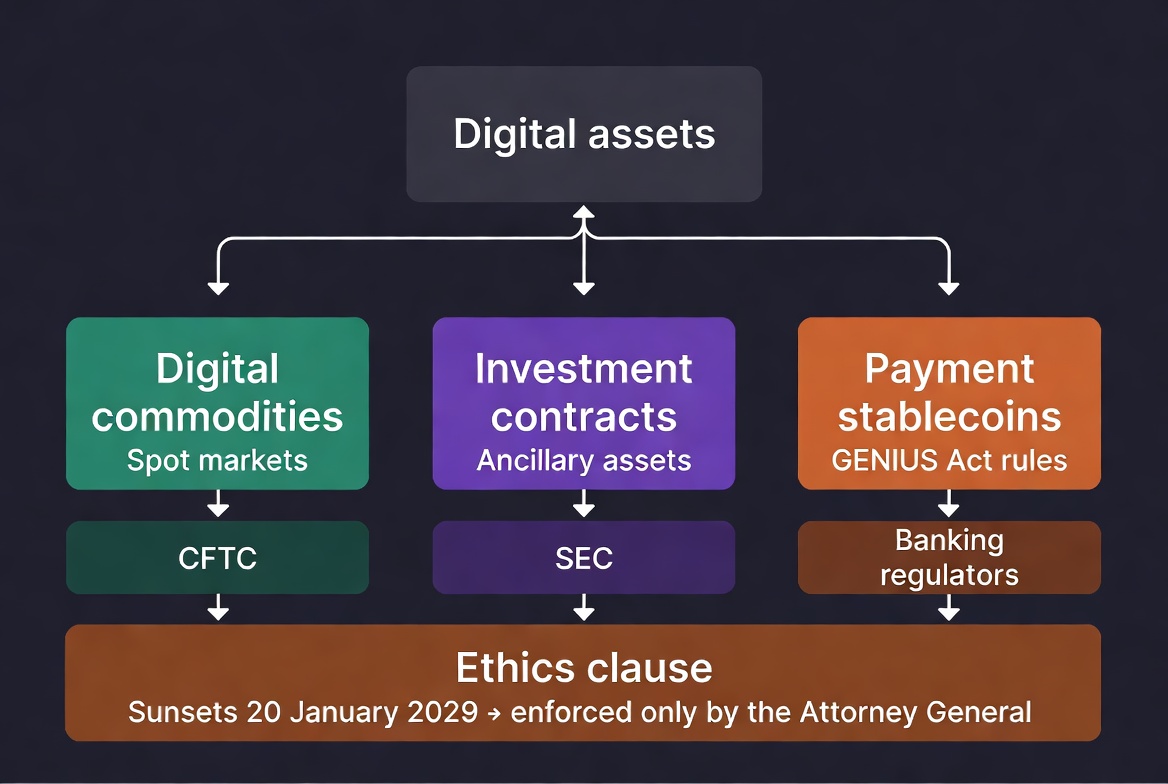
The merged text released on 22 July runs to roughly 616 pages. The core of it is a jurisdiction split. Spot markets in digital commodities go to the CFTC, investment contracts and ancillary assets stay with the SEC, and payment stablecoins fall under banking-style rules built on the already-enacted GENIUS Act. Exchanges, brokers and dealers would register with the CFTC.

Around that sit the provisions people actually argue about. A fundraising exemption lets projects raise up to $50 million a year and $200 million lifetime without full SEC registration. Intermediaries become financial institutions under the Bank Secrecy Act. Non-custodial developers get explicit protection from registration purely for writing code. Interest-like yields on idle stablecoin balances get banned while rewards tied to actual transaction activity survive. Most of it takes effect 360 days after enactment.

Worth noting what it is not. It does not touch tax treatment. Crypto remains property in the eyes of the IRS either way.


The Fight Is Not About Crypto

President Trump's 2025 financial disclosure showed roughly $1.4 billion in crypto-related income. About $636 million came from the $TRUMP meme coin and nearly $800 million from World Liberty Financial, the DeFi platform his family co-founded. A separate July disclosure tied more than $1 billion in income to his crypto ventures over the past year.

Democrats' position is structural rather than symbolic: they argue you cannot build a federal framework for an industry that produced the sitting President's single largest income stream without enforceable rules on his continued participation in it.

The White House agreed to ethics language that bars the President, Vice President, certain members of Congress, covered officials and their spouses from issuing or sponsoring a digital asset for consideration while in office, with a divestiture or blind trust requirement kicking in a year after enactment. Officials could still own crypto and would have to disclose sales.

Two details explain why that has not closed the deal. The ban sunsets on 20 January 2029, which is the end of the current presidential term, something we covered when the clause first appeared. And enforcement sits solely with the Attorney General, not state attorneys general and not private parties. So the restriction on the President expires when he leaves office and is enforceable in the meantime only by his own appointee.

Seven crypto-friendly Democrats rejected it. Angela Alsobrooks, Cory Booker, Catherine Cortez Masto, Ruben Gallego, John Hickenlooper, Mark Warner and Raphael Warnock said in a joint statement that the Republican text falls short, citing ethics alongside consumer protection, illicit finance, market integrity and DeFi regulation. Elizabeth Warren put it more directly, saying that whatever it is called, a provision that does not stop the President profiting from crypto is not an ethics provision.

Gallego, one of only two Democrats who backed the bill in committee, described the returned draft to Politico in language we will not reprint and said it was not a serious effort. He is now working on a counteroffer with Republican Thom Tillis.

Deadlines like this move fast.

We track what actually happens on the calendar, not what gets promised on it.

Subscribe

The Vote Might Happen Anyway, and Not to Pass

On 30 July, Treasury Secretary Scott Bessent publicly demanded an immediate floor vote, calling the bill floor-ready and accusing Senate Democrats of choosing politics over American leadership. Lummis amplified it, pointing to more than a hundred compromises already made and to the Fraternal Order of Police reversing its earlier opposition after the DeFi provisions were revised.

Thune has signalled he may bring the bill to the floor without the votes secured. That reads more as an election-year manoeuvre than a legislative one. Forcing senators to take a public position on crypto regulation months before November has value to Republicans whether or not the bill clears.

The risk is that it burns the negotiation. Cynthia Lummis, one of the Republican negotiators, posted that after nearly eleven months of giving almost everything asked of them, she does not know what else her Democratic colleagues need. Reporting on the talks suggests a forced vote on a text Democrats have already rejected could cause a rift that does not heal.


What the Market Thinks

Prediction markets have been brutal about this all year. Polymarket odds on CLARITY becoming law in 2026 peaked above 80 percent in February, hit a record low near 24 percent in mid-July, briefly recovered to around 45 percent when the updated text was expected, and have settled in the low-to-mid 30s as the ethics deadlock hardened. Galaxy Research cut its own estimate to 50 percent.

Worth noting what did not move those numbers. A direct public appeal from the President in mid-July produced no upward move at all, which tells you traders read the binding constraint as Democratic votes rather than presidential enthusiasm.


What Happens If It Slips

Failure before recess does not kill the bill. It pushes it into a September calendar with less momentum and then into an election year, where controversial votes get harder. Estimates of the delay range from 2027 to considerably longer. Lummis has warned that failure this year could push comprehensive federal rules out to 2030, after a Congress nobody has met yet is seated.

In the meantime the rules come from agencies rather than statute. The SEC and CFTC issued joint interpretive guidance on 17 March 2026 classifying sixteen digital assets under a five-category taxonomy, and the SEC has said it is prepared to write crypto rules if Congress does not. That is the part the industry actually fears, because interpretive guidance is not law. Any future administration can rescind it, and the whole framework reverts to enforcement discretion overnight.

Which is the real stake here, and it has little to do with this month. A statute is durable. Guidance lasts exactly as long as the people who issued it.


What to Watch This Week

One thing decides it: whether Thune files cloture on a motion to proceed before the chamber leaves. A filing typically sets up a vote two session days later, and without one there is no summer vote at all.

After that, watch whether the Gallego and Tillis counteroffer produces text the White House will accept, and whether any of the seven Democrats move publicly. If the window closes, the thing to track through autumn is whether leadership tries to attach CLARITY to must-pass year-end legislation. Lobbyists have floated that route in trade press. No senator has confirmed it.


Sen. Lummis (primary source) — Merged CLARITY Act text, released 22 July 2026

CoinDesk — Senators Ready to Send Stricter Ethics Rules on Trump's Crypto Ventures to White House

The Hill — Crypto Bill Faces Democratic Backlash Over New Ethics Rules

CoinDesk — US Senate Puts Off Crypto Clarity Act as It Focuses Limited Bandwidth Elsewhere

Bitcoin Magazine — Senate Democrats Reject Clarity Act Ethics Rewrite

Crypto News — CLARITY Act Senate Delay Drops 2026 Odds

Tools We Use

Kraken — Spot and futures on BTC, ETH, and 200+ assets.

Trezor — Cold storage. No internet connection required.

This is market commentary, not financial advice. Nothing here is a recommendation to buy or sell any asset. Do your own research.
Nobody Has a Safe Place to Put It: What Coldcard Actually Proved

BitBrainers - Nobody Has a Safe Place to Put It: What Coldcard Actually Proved

By BitBrainers Editorial

Coinkite shipped the code that lost other people's money, and nothing in what follows takes that off them. But the same category of failure has already hit the other side of the argument, the exchanges, and it hit harder. Blaming one company is correct and it is not sufficient. There is no side of this that is actually safe. Only different ways to lose.

The Number That Should Have Been the Headline

In the first half of 2026 the crypto sector recorded a record number of hacks, 207 by TRM Labs' count, most of them smart contract exploits. But the money did not follow the count. Infrastructure and key-management failures were about 15 percent of incidents and roughly 76 percent of the money stolen.

Coldcard sits in the second group, and so does every exchange breach in that same data. The exposure begins at the exact place the industry keeps losing the most money, which is how a key gets made and who holds it. That is not an obscure corner of the product. For a device whose entire purpose is generating and protecting a key, it is the product. For a custodian, it is the whole job.

We do not sell a safe answer here.

We read the failures honestly and tell you what they actually mean. That is the whole newsletter.

Subscribe

Why This Keeps Happening to Regular People

The people who lost coins on Coldcard were not careless. Many followed the exact advice the most respected names in Bitcoin were giving. The device sat on recommended-wallet lists for years. Trusting the consensus pick is not negligence.


This Was Coinkite's Failure, Start to Finish

The firmware was theirs. The change that routed seed generation away from the hardware random number generator, the device's only source of real entropy, and into a predictable software fallback went out in March 2021 under their name, in a product sold on the single promise that it would generate a key no one could guess. CEO Rodolfo Novak has said the company takes full accountability and that its review process failed to catch it. That much is not in dispute.

The context deserves more attention than it is getting. Coldcard was GPL-licensed until a competitor, Foundation, built a device on that code. Novak said publicly that he regretted the license. Coinkite moved to MIT plus Commons Clause, blocking competing derivatives, and stripped out the crypto libraries inherited from Trezor. Foundation has published a timeline showing the entropy bug entered in the same 120-file commit that removed those GPL dependencies. Foundation is a competitor with an obvious interest in that framing, but the commits are public and the dates line up.

The licensing choice has a second cost that nobody priced at the time. Source-available is not open source. Under the Commons Clause, other developers could read the code but could not legally build on it, which quietly thins out the population of people with any reason to read it closely. Five years is a long time for a seed generation routine to go unexamined in a Bitcoin product, and the license is part of why.

Then there is the response. Coinkite's first advisory on July 30 told Mk4, Q and Mk5 owners they were not affected. That was wrong, and the advisory had to be expanded the next day. In the interval, an attack was actively running and people with newer devices were reading an official statement telling them to stand down. One prominent developer publicly told Novak he had spread misinformation and said someone he knew personally had been robbed from a Mk4 seed within hours of that advisory. Samson Mow ended up telling people to migrate off every Coldcard model regardless of version, because the vendor's own guidance could no longer be relied on.

One more detail worth noting, because the week's commentary got it backwards. Coinkite's minimal data retention was treated as the reason it could not warn its own customers. In fact the company has now said it emailed every address it could reach through its store and newsletter systems, and its own store notice explains that Canadian law requires eight years of business records, so names and addresses were blanked while the email field was kept. Reaching customers during an active theft is the right call. It also means the privacy posture that was part of the pitch was never quite what buyers understood it to be.

Novak's other public framing was that the bug was likely found using AI, calling it a sober reality of the new paradigm. Read plainly, that is a company whose code lost roughly $88 million pointing at the tool that found the flaw rather than at the five years in which it did not find it itself. We covered that response in detail in our breakdown of Coinkite's statement.

The deeper issue is that the security model was never built for a normal person. Entropy bits, firmware version tracking, BIP-39 passphrases, multisig quorums, dice rolls to seed your own randomness. That is a specialist's checklist wearing consumer packaging, and most people bought the packaging.


It Is Not Over, and That Is the Point

The first wave was a clean $70 million sweep in 41 minutes. By August 2, Galaxy Research was tracking three waves totalling 1,367 BTC, roughly $88.6 million, across 4,585 addresses. The number has moved every day since the story broke, and it will likely move again after this is published.

Watch the direction of travel. The first wave went after the largest balances, pulling $30 million in ten minutes. The third is emptying wallets worth a few thousand dollars each. That progression only makes sense if the operator holds a long list of compromised seeds and is working down it by value, monetising the tail after the whales are gone.

The third wave also broke the fingerprint. The first two shared a hardcoded fee and identical batching, which is how researchers linked them. The third uses more complex, harder-to-trace patterns, and Galaxy says it cannot confirm the same operator is behind all three. Either the attacker is adapting, or others have worked out the same flaw independently. Neither is reassuring.

The reason this keeps going is structural. Coinkite's emergency firmware cannot repair a seed that was already generated. Every vulnerable seed still holding funds stays vulnerable until its owner moves the coins, and Galaxy has warned that future sweeps need not resemble the ones already mapped. This is not an incident that concluded. It is an exposure that stays open until every affected person acts, and most of them do not know they are affected.


So What Does a Normal Person Actually Do

Watch what has happened on the timelines since. Within two days, people who had just seen a consensus recommendation fail were issuing new consensus recommendations. Name a replacement device, argue that the answer is firms large enough to employ cryptographers, move on. Almost none of it comes with more verification than the advice that put Coldcard on every recommended-wallet list to begin with.

That is the mechanism, and it is running again right now. The problem was never that people picked the wrong brand. It was that a brand recommendation was ever load-bearing for something this consequential.

So the honest answer is that there is no zero-risk option, and anyone selling you one is selling something. What exists is a set of trade-offs you get to choose between with open eyes.

Self-custody removes the counterparty who can freeze or lose your funds, and hands you the entire job of key security, firmware, and backups. An exchange removes the technical burden, and reintroduces the counterparty, the honeypot, and the interface you cannot see behind. Both are real risks. Neither is theoretical.

The most defensible posture is not picking a winner. It is refusing to concentrate. Do not put everything on one device, one vendor's firmware, one exchange, or one signing method. Spreading holdings across independent failure modes will not stop a loss. It stops a single loss from being total.

For anyone rebuilding after this, the concrete version is keys split across manufacturers, a Trezor hardware wallet beside a different vendor in a multisig quorum. Not because that vendor is trustworthy. Because no single vendor has to be.


Why This Does Not End With Everyone in Custodians

Follow the argument to its usual conclusion and you get: most people cannot do this safely, so most people should hand their coins to someone who can. A lot of this week's commentary lands exactly there, and the ETF and treasury-company flows suggest the market already agrees.

The objection is concentration. Enough Bitcoin in a few custodians rebuilds the seizure risk the thing was built to route around. What stops that from being terminal is a property gold never had. You can leave. Any holder can open a wallet, demand settlement, and have final possession in minutes, globally, for a few dollars. Most gold was never in its owner's hands, and you could not demand it be moved from London to Singapore this afternoon.

So custody concentrates only as long as the custodians stay worth using. The exit is what keeps them honest, and the exit only exists because self-custody remains possible for anyone who wants it. That is the case for keeping these skills alive even in a week that made them look dangerous.


The Part Nobody Wants Printed

Here is the sentence the industry avoids. In its current form, self-custody asks for a level of technical fluency that most people holding Bitcoin do not have and should not be expected to acquire overnight.

Read the failures, spread the risk, and distrust anyone who tells you one product ends the problem. That is not a satisfying conclusion. It is the accurate one, and the accurate one is the only kind worth publishing.


TRM Labs — H1 2026 Crypto Hacks Reach Record High as Losses Fall Below $1 Billion

Crypto Briefing — Crypto Records Most Hacked Half-Year Ever With 212 Exploits and $1.1 Billion Stolen

CoinDesk — How Bitcoin Cold Wallets Lost $70 Million in an Attack That Never Touched the Devices

CoinDesk — Bitcoin Cold-Wallet Attack Spreads to 4,500 Addresses as Losses Near $89 Million

The Block — Coinkite Issues Warning for Coldcard Mk3 Users Amid 594 BTC Theft Reports

Forbes — Urgent Warning Issued After Sudden Spread Of Massive Bitcoin Attack

This is market commentary, not financial advice. Nothing here is a recommendation to buy or sell any asset. Do your own research.
Saturday, August 1, 2026

Your Hardware Wallet Might Already Be Broken

BitBrainers - Your Hardware Wallet Might Already Be Broken

By BitBrainers Editorial

It is tempting to read the Coldcard drain as a single company's mistake. That reading is too comfortable. In the space of about two months, three separate cryptographic flaws surfaced in crypto code that had all passed review, all of them years old, all found in a narrow window. Coldcard is the loudest one. It is not the only one, and the pattern is the actual story.

Three Failures, Three Layers

Start with the timeline, because the clustering is the point. In late May, security firm Coinspect disclosed a flaw it named Ill Bloom: a broken random number generator in certain mobile software wallets that made recovery phrases guessable. Affected wallets dated back to 2018. At least $5 million was drained, most of it Bitcoin.

Around the same window, Zcash disclosed a flaw of a different kind entirely. Not in a wallet, but inside the mathematical circuit that proves its private transactions are valid. A gap in the proving code that could, in theory, have allowed counterfeit ZEC. Zcash ran an emergency hard fork on July 28 to wall off the affected pool.

Then Coldcard, at the end of July. The same failure family as Ill Bloom, weak seed generation, but in the hardware wallets people had been told to trust precisely because software wallets kept failing. Roughly $70 million gone in 41 minutes.


The Detail That Ties Them Together

Here is the part worth sitting with. When Coinspect disclosed Ill Bloom, it said hardware wallet users appeared to be safe. That was true, for that flaw. It was also the advice that pushed exposed users toward hardware devices.

Weeks later, the hardware devices had their own entropy failure. The safe harbor from one bug was the epicenter of the next. Nobody was lying. The ground simply kept moving.

These were not the same bug or the same team. What they share is a category: old cryptographic code, sitting in production for years, doing something subtly wrong that nobody caught until someone went looking with the right tools.

Patterns matter more than incidents.

We connect the failures nobody else is connecting. Get the next one before it is obvious.

Subscribe

Why Old Code Is Suddenly Dangerous

For years, the industry treated survival as proof of safety. If a wallet or a library ran for five or ten years without incident, it was assumed sound. That assumption was always weaker than it looked.

A vulnerability that was never worth the enormous manual effort to find can become worth finding the moment that effort drops. Reading an unfamiliar codebase line by line, tracing dependencies, spotting one inverted check among thousands, used to take specialist time most attackers would not spend.

Coinkite said it plainly about its own bug: the code had been public since 2021, and the company has to assume someone used AI to review old versions of the firmware and found what human auditors, including a leading AI model Coinkite itself ran weeks earlier, had missed. We covered that admission in detail in our breakdown of Coinkite's response.

The uncomfortable implication is not about one vendor. It is that the cost of finding dormant bugs has fallen for everyone, defenders and attackers alike, and the attackers only need one.


What Is Actually Exposed

Bitcoin Core itself is not the worry here. It is probably the most reviewed open-source code in existence, with hundreds of people picking apart every proposed change. The danger lives in the sprawl around it.

Wallets, firmware, signing libraries, bridges, exchange infrastructure, swap tools. An enormous surface of code, most of it reviewed far less thoroughly than Core, much of it depending on the same handful of underlying libraries. Ill Bloom, Coldcard, and the Zcash circuit flaw all lived in that surrounding layer, not in a base protocol.

That is where the next one will come from too. Not a break in Bitcoin's core math, but a forgotten piece of the ecosystem that held enough money to make the search worthwhile.


What This Changes for You

The takeaway is not to panic or to abandon self-custody. It is to stop treating any single product's track record as a guarantee. Five clean years means the bug was expensive to find, not that it was never there.

The practical response is the same discipline that survives every one of these events: do not concentrate. Spreading holdings across independent devices, vendors, and methods will not prevent a flaw. It stops any one flaw from taking everything.

None of these three incidents touched a properly diversified setup for its full value. That is not luck. It is the one defense that works when the thing you trusted turns out to have been broken since the day you bought it.


The Hacker News — Attackers Exploit 'Ill Bloom' Vulnerability to Drain Over $5 Million From Cryptocurrency Wallets

TechTimes — Zcash Ironwood Launches Tuesday: Supply-Verification Checkpoint Closes Four-Year Flaw

CoinDesk — How Bitcoin Cold Wallets Lost $70 Million in an Attack That Never Touched the Devices

This is market commentary, not financial advice. Nothing here is a recommendation to buy or sell any asset. Do your own research.
Saylor's Company Lost 8.3 Billion on Paper

BitBrainers - Saylor's Company Lost 8.3 Billion on Paper

By BitBrainers Editorial

Strategy reported one of the largest quarterly losses in its history on Thursday. Michael Saylor's company also added more Bitcoin than almost any quarter before it. Both of those sentences are true, and reading only the first one is how most of the coverage got this wrong.

The Loss Everyone Is Reading Wrong

Strategy's operating loss for Q2 came in around $8.3 billion, and roughly $8.32 billion of that was a single line item: a non-cash, unrealized write-down on its Bitcoin holdings under fair-value accounting.

That accounting rule, formally ASC 350-60, took effect for public companies last year. It requires Bitcoin holdings to be marked to market every quarter, meaning the balance sheet now moves with the price whether or not a single coin gets sold.

Nothing left the company because of this loss. It is a valuation entry, not a wire transfer. The reported net loss figure varied slightly across outlets, some cited $8.6 billion, others closer to $8.2 billion, but the underlying driver was the same $8.32 billion mark-to-market swing every time.


What Strategy Actually Did With the Quarter

While the accounting line went negative, the company added 83,901 BTC during the quarter at an average price near $75,500, bringing total holdings to 843,775 BTC. That is roughly 4 percent of every Bitcoin that will ever exist, by the company's own count.

Holdings are up 25 percent since the start of 2026. More telling is the metric Strategy wants shareholders watching instead of GAAP earnings: Bitcoin per share, which rose from 201,170 to 210,824 satoshis, a 5 percent gain in a single quarter, despite meaningful share dilution from ongoing capital raises.

The stock moved higher in the after-hours session following the print. Investors appear to have looked past the headline loss to the accumulation number underneath it, which is exactly the read Strategy has spent two years training the market to make.


Q2 2026 at a Glance

The headline loss and the accumulation number, side by side.

METRIC Q2 2026
Total Bitcoin holdings 843,775 BTC
Bitcoin added this quarter 83,901 BTC
Average purchase price ~$75,500
Share of total Bitcoin supply ~4%
Holdings growth since Jan 1, 2026 +25%
Bitcoin per share (BTC yield metric) 210,824 sats (+5% QoQ)
Software revenue $122.4M (+6.9% YoY)
Operating loss ~$8.3B
Unrealized Bitcoin write-down (non-cash) $8.32B
Convertible debt outstanding $8.21B → $6.71B
STRC preferred stock (target $99-100) ~$89.50

Reported net loss varied slightly by outlet, roughly $8.2B to $8.6B, depending on which line items were included. The operating loss and the $8.32B Bitcoin write-down were consistent across every source.

The headline number is rarely the real one.

We read past it every time. Get the actual story in your inbox.

Subscribe

Saylor's Framing, and Why It Isn't Wrong

On the call, Executive Chairman Michael Saylor described Bitcoin as the winner of the "digital capital network race" and said the company's real opportunity now sits in building credit infrastructure on top of it, not in the software business that once defined MicroStrategy.

That is not new bravado. It is the same thesis the company has run since it went all-in on Bitcoin years ago. What changed is that fair-value accounting now forces that volatility onto the income statement every single quarter instead of leaving it in a footnote.

The framing held while the accumulation was real. What changed this quarter is that the company stopped treating accumulation as automatic, which makes the credit-infrastructure language less a vision statement than a description of where the balance sheet is actually headed.


The Part of the Story That's Actually Risky

Strategy's preferred stock, STRC, was trading near $89.50 against a $99 to $100 target range. The company is running a $1 billion buyback, with roughly $975 million still unused, aimed at getting STRC back to par by a September 8 target date.

And the buying has stopped. Strategy has now gone five consecutive weeks without a Bitcoin purchase, its longest confirmed pause in nearly two years, with holdings flat at 843,775 BTC while the ATM programs kept running. Dollar reserves stood at $3.75 billion as of 26 July.

On the debt side, the company repurchased $1.5 billion of convertible notes at an 8 percent discount, cutting convertible debt outstanding from $8.21 billion to $6.71 billion. That is a genuine deleveraging move sitting inside the same quarter as the headline loss.

One more fact worth stating plainly: Rosen Law Firm opened a securities investigation in June into whether Strategy and its executives made materially misleading statements about the Bitcoin strategy and the risks in its preferred securities. No complaint has been filed as of this writing, and an investigation is not a finding of wrongdoing. It is, however, a fact of the current situation and belongs in any honest account of it.


The Part That Actually Changed

The accounting loss led every headline. The more consequential disclosure came from the call itself, and it got far less attention.

President and CEO Phong Le said Strategy will sell Bitcoin whenever management considers it advantageous, and that investors should expect it may do so going forward. That is not hypothetical. The company already completed its largest-ever Bitcoin sale earlier this year, roughly 3,588 BTC, under what it calls its BTC Monetization Program, with proceeds going toward preferred dividend obligations.

Management also said future capital raises will no longer flow entirely into Bitcoin. Proceeds will be allocated dynamically between Bitcoin and US dollar reserves depending on market conditions, liquidity needs, and corporate obligations. Bitcoin-backed borrowing was explicitly ruled out, citing counterparty and margin risk.

For a company whose entire identity was built on never selling, that is the story. The automatic link between raising capital and buying Bitcoin is gone. Investors can no longer read a share sale as a coming purchase, and the company has told them in plain terms to expect sales.


What This Sets Up

Strategy's structure now leans on Bitcoin's price to service two separate obligations on two separate timelines: defending STRC's par value by September, and meeting convertible note put dates further out in 2027. Both make the company more exposed to a sustained drawdown than "they just bought more Bitcoin" suggests on its own.

STRC pays a 10 percent annual dividend, distributed monthly. That obligation keeps running regardless of Bitcoin's price. The September 8 target is not a soft goal. If STRC stays below par through that date, it signals to the market that the preferred dividends are not comfortably covered by the Bitcoin treasury model, which feeds directly into the 2027 convertible note put dates where holders can demand repayment. The dividend is not the risk. The sequence is.

This quarter is effectively the template other Bitcoin treasury companies will either follow or avoid. Anyone who wants Bitcoin exposure without taking on that layered corporate debt and preferred-equity structure has a simpler option: holding it directly through a platform like Kraken rather than through MSTR's equity.

The real test is not this quarter's accounting print. It is whether Bitcoin's price stabilizes enough for STRC to reach par by September 8. That date matters more to Strategy's near-term stability than anything in Thursday's headline number.


Coinpedia — Strategy Ends Its Buy Every Dip Bitcoin Strategy, Here's What's Replacing It

FinanceFeeds — Strategy Says It Will Continue Selling Bitcoin and No Longer Allocate All New Capital to BTC Purchases

Yahoo Finance — MicroStrategy Q2 2026: Bitcoin Accumulation Accelerates Despite Accounting Loss

Investing.com — Earnings Call Transcript: MicroStrategy Q2 2026 Loss Deepens as Bitcoin Bets Weigh

CoinSpeaker — Strategy Q2 2026: $8.6B Loss Driven by Bitcoin Accounting

TheStreet — Strategy Misses Q2 Earnings Estimates by a Wide Margin

TechTimes — Strategy Q2 Earnings Due Tonight: $8.3B Bitcoin Loss and Capital Model Under Test

This is market commentary, not financial advice. Nothing here is a recommendation to buy or sell any asset. Do your own research.
Coinkite Blames AI for the Bug, and the Attacker Left a Paid Account Behind

BitBrainers - Coinkite Blames AI for the Bug, and the Attacker Left a Paid Account Behind

By BitBrainers Editorial

Three days ago, Coldcard's entropy bug was one bad number. It has since split into two disputed totals, a vendor admission about AI, and a paper trail that ends at a blockchain data provider's billing account. Here is what actually changed since the last update, and why the total will likely keep moving.

Two Firms, Two Totals, Same Bug

Chainalysis put the damage at roughly $38 million as of Friday, tracing about 500 wallets swept in a tight 25-minute window. Galaxy Research and Block's own engineering team came in far higher: 1,196 addresses, 1,082.65 BTC, worth close to $70 million, across a wider 41-minute span.

The gap is not a disagreement about the bug itself. It is a disagreement about which transactions belong to the same attacker, since the two firms drew the boundary of "this event" differently and neither has finished counting.

Independent trackers were already citing a higher total by Saturday morning, unconfirmed by either firm. If you want the original entropy breakdown and the first 594 BTC sweep, our July 31 breakdown covers that from the start.


What We Know So Far

Four consolidation addresses account for most of the confirmed total. None have moved since the sweep.

CONSOLIDATION ADDRESS BTC STATUS
bc1qq85v2c9...cu9r 562.02 ● unmoved
bc1qx76cae2...fhe3 398.48 ● unmoved
bc1q8jy96fe...tp3q 89.62 ● unmoved
bc1qnk4zh9q...fecp0 32.45 ● unmoved

That's roughly 1,082.5 of the 1,082.65 BTC Galaxy Research attributes to the full sweep, accounted for across four wallets. Figures per Galaxy Research's on-chain mapping, corroborated by Block. Verify any balance directly on a block explorer rather than a third-party dashboard.

The Attacker Went for the Largest Wallets First

Chainalysis's timeline adds the most interesting new detail. In the first 10 minutes, the attacker had already pulled roughly $30 million, hitting the largest wallets before working down the list.

Three of the ten biggest affected wallets held at least 10 BTC each. That is not opportunistic scanning. The list was sorted by value before the first transaction was broadcast.

Sorting by balance ahead of time means the attacker had visibility into wallet holdings before touching a single signing key, which points to a reconnaissance phase that likely ran for weeks.

Numbers like this change fast.

Get the reconciled totals and the next disclosure the moment they land.

Subscribe

Coinkite's Own Explanation Is the Uncomfortable Part

Coinkite has now said it has to assume "someone used AI to review previous versions of our firmware" to find the bug, since the code has been sitting in public view since 2021.

The company also disclosed it ran a leading AI model over its own codebase a few weeks before the attack happened. That review did not flag the issue either.

Set that next to the forum's own technical read: a #define versus #ifdef mismatch, invisible unless someone traced the macro logic line by line. Five years of public code, and the people paid to audit it were not the ones who found it.


A Billing Account May Be the Attacker's Only Mistake

Block's Bitkey engineering lead, Clay Garrett, said investigators confirmed "the operator used a paid account at a well-known blockchain-services provider" to query source addresses during the sweep.

The provider's internal logs reportedly matched the timing and sequence of the attack closely enough that Block is calling the finding confirmed rather than suspected. Authorities have been notified.

None of this means an arrest is close. The cryptographic work here was close to flawless, and the target list was sorted by balance before a single key was touched. What the operator did not avoid was one ordinary point of contact with a company that keeps records.


What Actually Changes If You Own One

Coinkite shipped mandatory patches: firmware 5.6.0 for Mk4 and Mk5, 1.5.0Q for the Q model. There is no patch for Mk3 or Mk2, because the fix is a new seed, not a firmware update.

Updating firmware does not make an old seed safe by itself. The actual fix is generating a brand new seed on updated hardware, verifying the receive address on-device, and testing with a small transaction before moving the rest.

If you are rebuilding anyway, this is also the moment to consider spreading the risk across manufacturers instead of trusting one vendor's firmware for everything, which is the whole case for something like a Trezor hardware wallet as a second device in a multisig setup.


The Bigger Argument This Reopens

Bitcoin Core developer instagibbs independently reproduced the vulnerability, which closes any remaining doubt that this is real. The technical story is essentially finished. The institutional one is not.

Analysts are already using the incident to argue that self-custody has quietly built up its own operational risk, the kind that nudges undecided holders toward regulated custodians and spot ETFs instead of a hardware wallet in a drawer.

Price barely moved through any of this. BTC held its key support level the whole time, which says more about how numb the market has gotten to security headlines than about how serious this particular one actually is.


CoinDesk — How Bitcoin Cold Wallets Lost $70 Million in an Attack That Never Touched the Devices

Bitcoin Magazine — Coldcard Bitcoin Thief Likely Used Top Blockchain Services Provider

Cybernews — AI Might Have Helped Hackers Steal $38M in Bitcoin

AMBCrypto — Coldcard Seed Flaw Linked to $38M Bitcoin Theft as Loss Estimates Continue to Rise

CoinDesk — Coldcard's $38 Million (So Far) Exploit Shakes Faith in Self-Custody, May Push Investors to ETFs

This is market commentary, not financial advice. Nothing here is a recommendation to buy or sell any asset. Do your own research.

The War in the Price of Everything

Illustration: a crude tanker on Gulf water. The strait Iran mined in February carries a fifth of the world's oil.

The War in the Price of Everything